
News
Tusker Achieves SOC 2 Type II Compliance
Tusker’s SOC 2 Type II certification reflects our commitment to data security, risk management and reliable IT services.
Cybersecurity
Tusker officially achieved SOC 2 Type II compliance in April 2026, marking an important milestone in our continued commitment to protecting customer data and maintaining strong internal security practices.
While several of the companies that came together to form Tusker had previously completed SOC 2 examinations, this is the first SOC 2 Type II attestation completed by the unified Tusker organization.
What Is SOC 2 Type II?
SOC 2 is a widely recognized framework developed by the American Institute of Certified Public Accountants. It evaluates how service organizations manage and protect customer information through their internal systems, policies and processes.
A SOC 2 Type II examination evaluates both the design of an organization’s controls and how effectively those controls operated over a defined period. This makes it an important measure of whether established security practices are consistently followed in day-to-day operations.
What This Means for Tusker Customers
For customers, Tusker’s SOC 2 Type II attestation provides independent validation of the controls supporting how we operate and safeguard sensitive information.
It demonstrates our ongoing focus on:
- Maintaining documented and repeatable security processes
- Identifying and managing operational risk
- Protecting customer and organizational information
- Monitoring the effectiveness of internal controls
- Continually strengthening our security practices
SOC 2 compliance is not a one-time exercise. It requires sustained attention, accountability and ongoing evaluation—all of which align with how Tusker approaches security for our own organization and the customers we support.
Practicing the Security We Recommend
As a technology and cybersecurity partner, Tusker helps organizations strengthen their environments, manage risk and prepare for evolving threats. Achieving SOC 2 Type II compliance reinforces that we apply the same discipline to our own operations.
It also reflects the work completed to bring multiple established organizations together under one shared set of Tusker policies, processes and controls.
Moving Forward with Confidence
Technology partners are often entrusted with access to critical systems, infrastructure and information. Tusker’s SOC 2 Type II attestation gives customers additional confidence that security and accountability are built into how we work.
As Tusker continues to grow and expand its cybersecurity capabilities, this milestone reinforces the strong security foundation supporting our organization and our customers.
Looking for a technology partner that takes security seriously? Contact Tusker to start the conversation.
Our Team
Industry Leaders
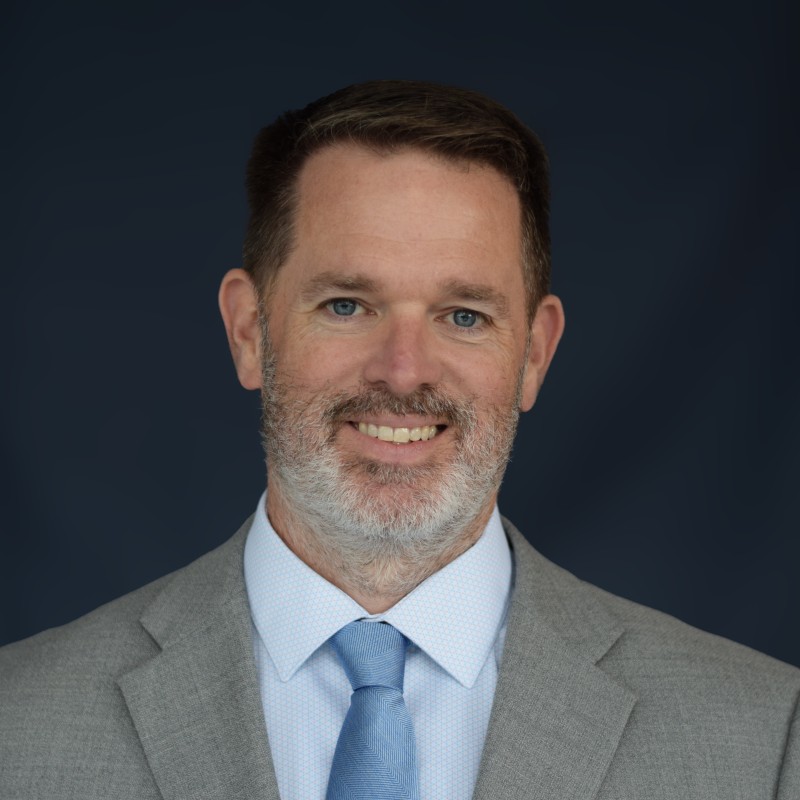
Matt Cox
Matt Cox is Tusker’s Information Security Officer and a Cybersecurity Consultant, helping organizations understand their risks and strengthen their security without added complexity.
Grow your bottom line with our tailored services.
Get in touch
Talk to us about how to transform your business.
View more
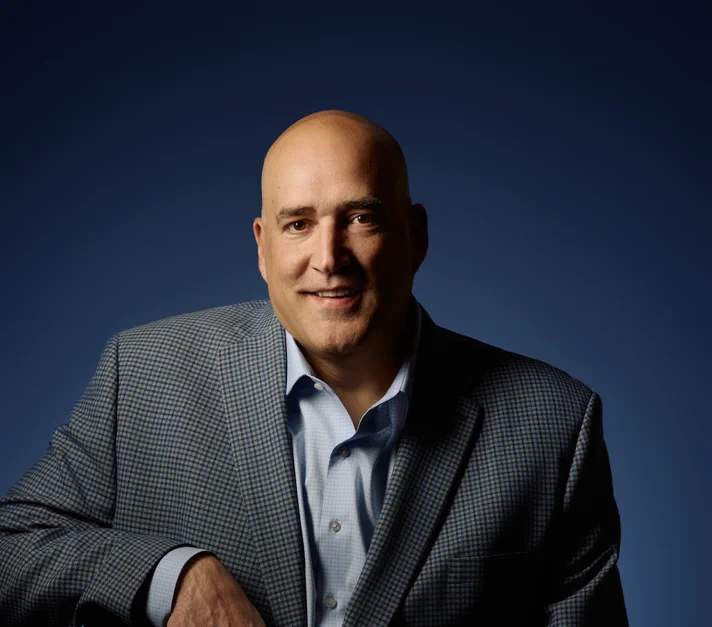
Matt Gaudio Named CEO of Tusker, a Fast-Growing National IT Solutions Provider
Matt Gaudio will Continue the Growth Strategy Led by Departing CEO Matt Zafirovski
Cloud Infrastructure
Four Resources to Simplify Video Infrastructure Planning
Practical tools to help you size storage, evaluate infrastructure, and select the right systems for video, analytics, and AI workloads
Cybersecurity
Tusker Achieves SOC 2 Type II Compliance
Tusker’s SOC 2 Type II certification reflects our commitment to data security, risk management and reliable IT services.